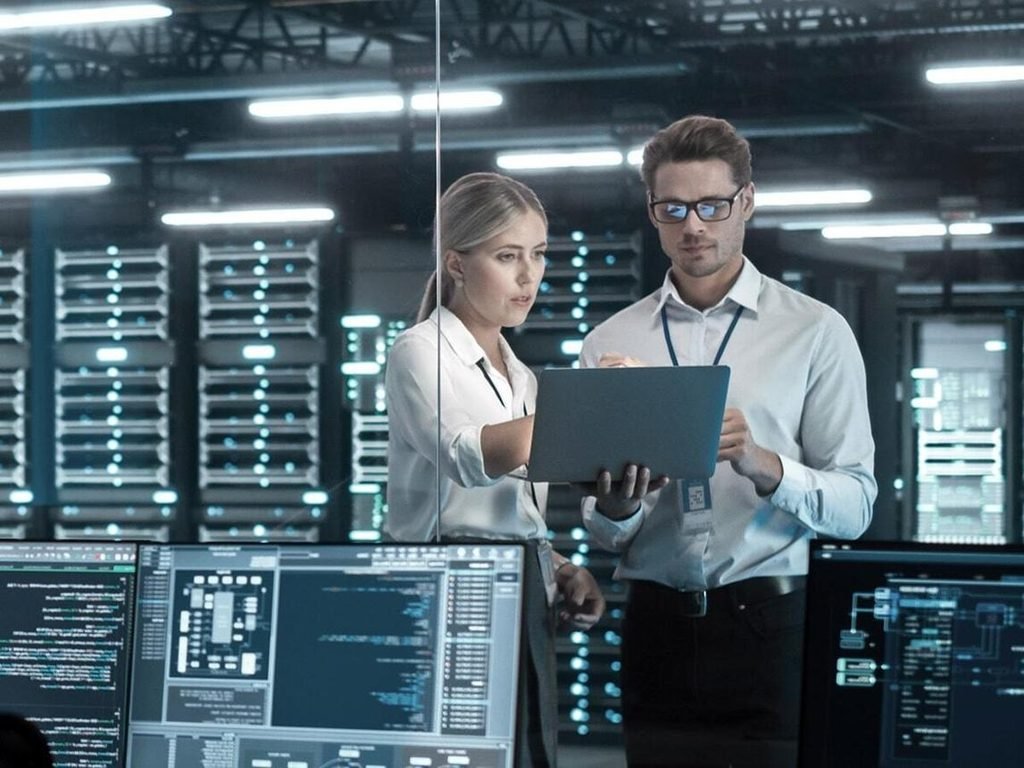
Confidential computing protects information while a computer processes it, rather than protecting it only during storage or transfer. This matters for businesses that handle customer records, financial details, medical information, or confidential company documents.
Traditional safeguards leave a gap when applications need to work with decrypted information. Confidential computing addresses that gap through protected execution environments, helping restrict access to data during active processing. It gives organizations another way to reduce exposure without abandoning cloud-based services.
Why Does Data Privacy Need Confidential Computing?
Data privacy concerns extend beyond stolen passwords or exposed databases. Information can face risks whenever applications process it. Administrators, compromised software, or other privileged access paths may create exposure if protections are inadequate.
Confidential computing adds a layer of defense at the processing stage. It helps organizations limit who can inspect information. That distinction matters for businesses handling information that cannot simply be replaced after a breach.
How Does Confidential Computing Work?
Confidential computing uses hardware-based trusted execution environments, often called TEEs, to create protected areas for running applications. These environments isolate selected operations from the surrounding system, limiting access to information processed inside them.
The application can decrypt and analyze information within this protected area without exposing it to every component that manages the server. Hardware checks and cryptographic verification help establish whether the environment can be trusted before sensitive workloads begin.
How Is Confidential Computing Different from Data Encryption?
Data encryption protects information in different states, but each state presents different technical requirements. Information stored on a disk can remain encrypted, and information moving between systems can travel through an encrypted connection. Processing usually requires applications to work with readable data.
Confidential computing helps protect information during that processing stage. It can complement existing data encryption methods by restricting access to information inside a protected execution environment.
Why Cloud Security Needs Another Layer of Protection
Businesses often depend on external providers for computing capacity, application hosting, storage, and analytics. These arrangements can reduce infrastructure costs, but they require organizations to decide how much access providers and administrators should have.
Traditional cloud security measures protect networks, accounts, applications, and stored information. Confidential computing addresses another concern: limiting access to data during execution, including in situations where infrastructure privileges could otherwise create risks.
For example, a financial services company might analyze customer transactions through a cloud-hosted application. Protected execution can help restrict exposure during that analysis, subject to the system’s implementation and its security limitations.
Which Industries Can Benefit from Confidential Computing?
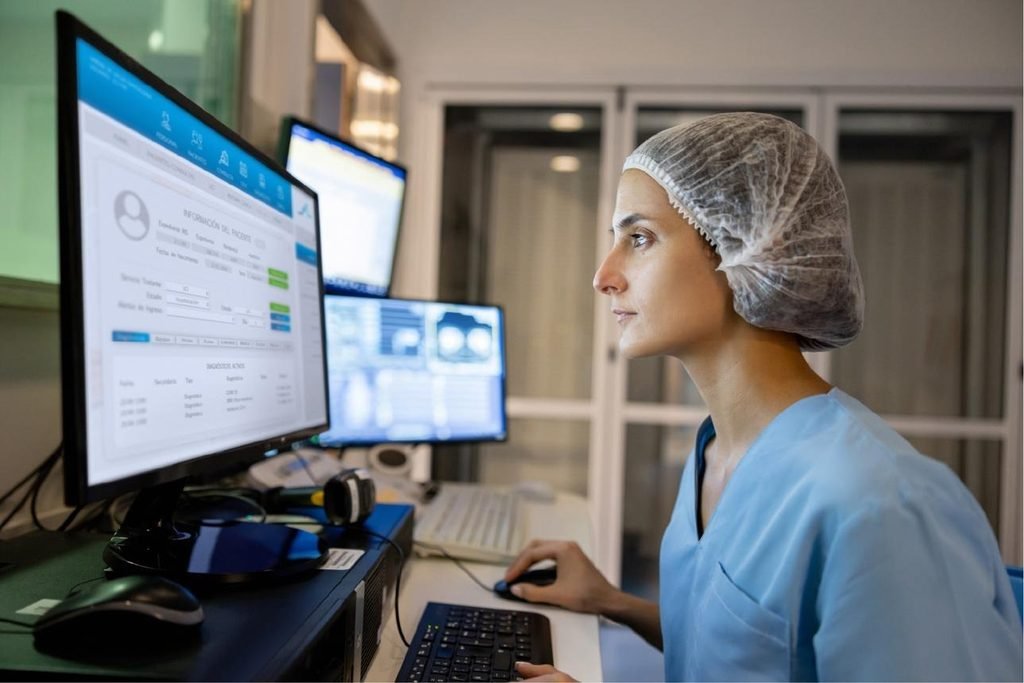
Healthcare
Hospitals and research teams process patient records, diagnostic results, and clinical research data. Confidential computing can help protect this information during approved analysis, particularly when several institutions collaborate on sensitive projects.
Banking and Financial Services
Banks handle transaction histories, credit assessments, and fraud investigations. Protected processing can reduce exposure when financial institutions share computing resources or analyze information across separate systems.
Technology and Artificial Intelligence
Technology companies can use confidential environments to process proprietary models, private datasets, and customer information. These safeguards may help teams collaborate without granting every infrastructure operator access to sensitive material.
Three Practical Ways to Assess Confidential Computing
Before introducing this technology, businesses should establish which information needs stronger protection and what threats the deployment must address.
- Identify sensitive workloads: List applications that process financial records, customer identifiers, intellectual property, or regulated information. Prioritize workloads where unauthorized access could create serious financial or legal consequences.
- Check hardware and provider capabilities: Ask which processors and trusted execution environments are supported. Review attestation procedures, software compatibility, key management, and the provider’s documented security limitations before choosing a deployment.
- Test the complete application: Run controlled tests to examine performance, recovery procedures, monitoring, and access restrictions. Include the security team in these tests so that technical limitations are documented before production workloads move.
What Challenges Should Businesses Expect?
Confidential computing can introduce hardware requirements, application changes, and additional operational work. Certain workloads may run more slowly, and applications that depend on unsupported instructions or services might need adjustments.
Sensitive data protection still requires careful management of encryption keys, user permissions, software updates, and application vulnerabilities. Protected execution does not automatically prevent phishing, compromised accounts or information leaks through poorly designed applications.
Where is Confidential Computing Heading?
Confidential computing is becoming relevant to projects that involve shared datasets, private artificial intelligence workloads, and collaboration between organizations that cannot freely exchange sensitive information. Its value depends on whether protected execution addresses a specific exposure that existing safeguards cannot adequately reduce.
As adoption grows, organizations will need clearer ways to verify security claims and assess compatibility across providers. Hardware protections must work alongside careful software development, access management, and independent security testing.
For businesses planning new cloud projects, this technology deserves consideration during architecture and procurement discussions, not only after a privacy concern appears.
Conclusion: Making Data Privacy Stronger During Processing
Privacy protection needs to cover information throughout its use, including periods when applications must read and analyze it. Confidential computing addresses this gap by restricting access to information inside protected execution environments. It can help businesses reduce exposure, though no single safeguard removes every security risk.
Adopting confidential computing makes the most sense when organizations identify clear threats, assess provider capabilities, and test the technology against their workloads. Combined with established security practices, it offers another practical way to protect sensitive information during processing.
FAQs
Could confidential computing help a small business using third-party software?
Yes, depending on the software provider and hosting arrangement. Ask the vendor whether protected execution is supported, which workloads use it, and what independent security documentation customers can review.
Does confidential computing affect application performance?
It can, depending on processor capabilities, workload size, and memory requirements. Benchmarking representative tasks before deployment helps teams estimate costs and determine whether additional hardware resources or application changes are necessary.
How can a business check a provider’s confidential computing claims?
Request independent security assessments, hardware specifications, attestation documentation, and incident procedures. Ask how the provider handles failed verification and whether customers can independently validate the environment.
What should companies ask before adopting confidential computing?
Ask which workloads qualify, how key access is controlled, and who investigates suspected exposure. Confirm whether the provider’s data privacy technology supports contractual requirements and whether audit evidence remains available throughout the agreement.
Can confidential computing protect information shared between business partners?
It can support collaborative analysis without exposing all underlying records to every participant. Businesses should assess secure cloud computing options, define permitted outputs, and agree on access rules before exchanging sensitive datasets.